Root / Jailbreak Detection
Detects rooted Android and jailbroken iOS devices with OS-level security removed.

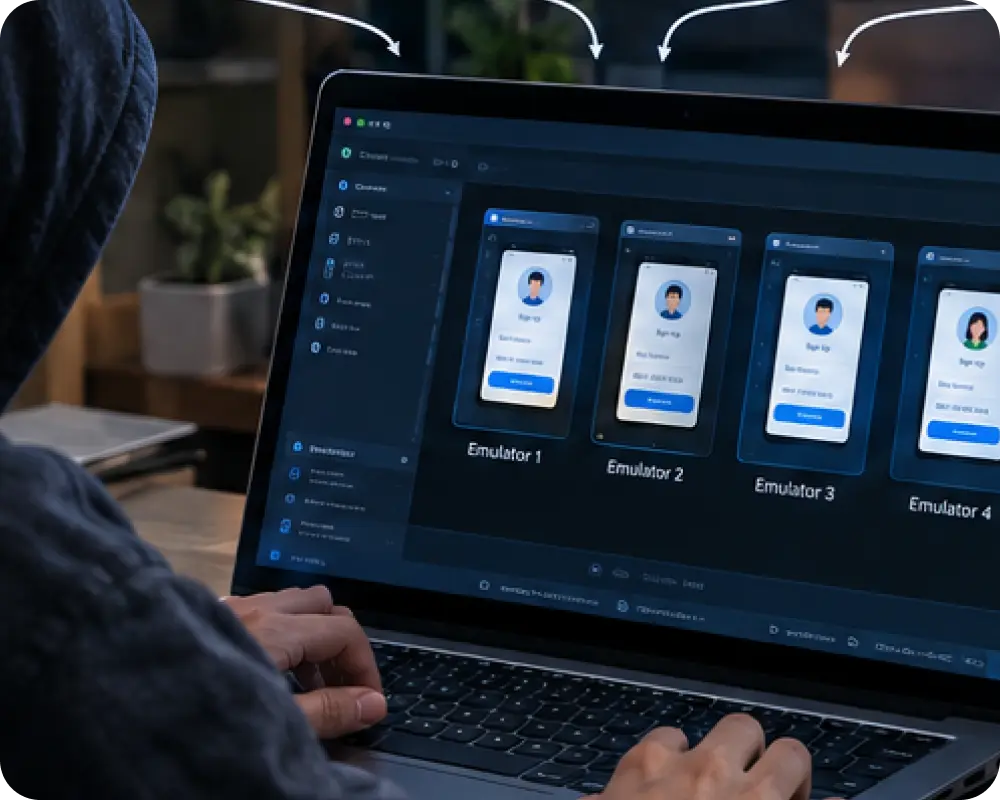
Block fraudsters before they attack. Verihubs instantly detects emulators, device tampering, and fake identities so zero fake users enter your app.

Fraud Prevention &
Account Security
Suspicious logins and ATO
Block compromised devices automatically before they can ever attempt to log in.
Fraudsters log in freely. You only notice after account takeovers happen.
Multi-Account & Fake Account
Detection
One device, many fake identities
Catch and stop multi-accounting instantly before any bonuses or rewards are claimed.
One device drains your promos using multiple fake profiles completely undetected.
KYC Strengthening &
Onboarding
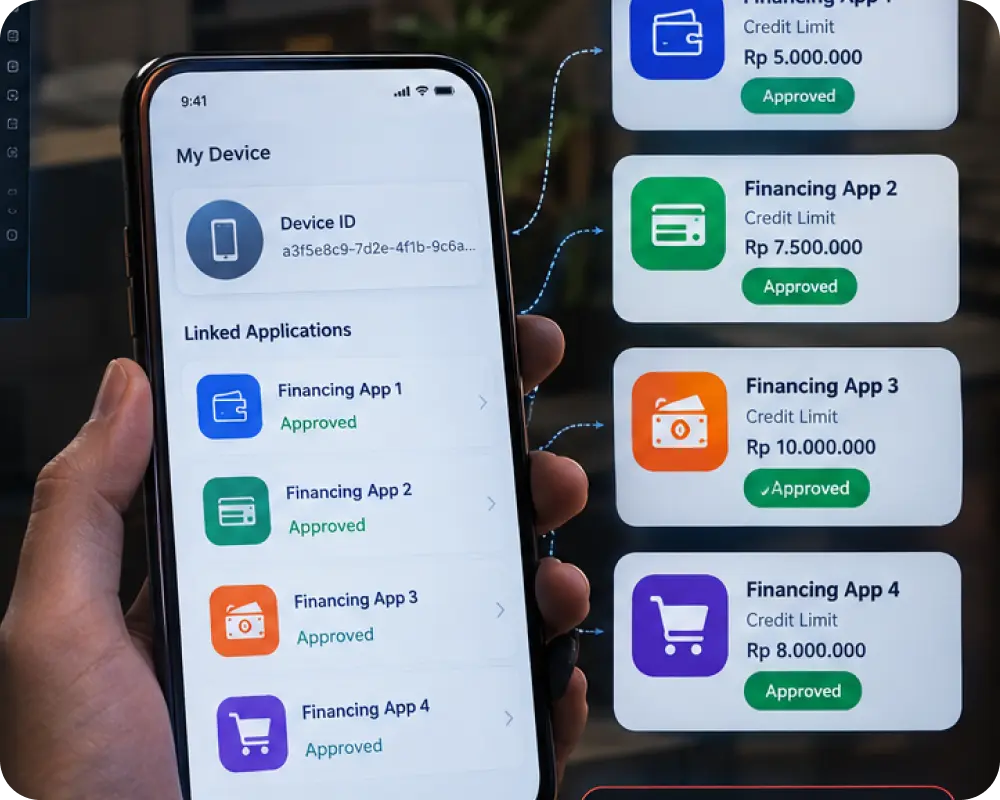
Device context at registration
Instantly verify device and location signals
before the user even fills in the first field.
Your KYC checks the ID document, but stays completely blind to device risks.
Why our Device Intelligence
How It Works
Every check below runs the moment your app opens, finished before the user even reaches your login screen.
Verihubs SDK activates silently in the background with zero loading screens or extra steps. Integrates in under 2 hours with no UX changes required.
Verihubs instantly checks for emulators, root/jailbreak, GPS spoofing, VPNs, and app tampering in the background—all before the user even reaches your onboarding form.
Receive a real-time device risk score before onboarding starts. Automatically block high-risk devices, send medium-risk to review, and pass trusted users instantly.
Use Case
Problems
Trading bots run on emulators to manipulate markets, rooted devices bypass withdrawal limits, and VPNs mask real locations to operate multiple fake accounts undetected.
Solutions
Detects emulators, root/jailbreak, VPN spoofers, hooking frameworks, and app tampering the moment the app opens. Active Call Detection also flags ongoing calls during login, trading, or withdrawals to help prevent social engineering fraud.
Use Cases: Account takeover • Fake accounts • Withdrawal fraud • Multi-accounting • Referral & bonus abuse • Social engineering fraud
Most fraud tools analyze behavior and identity, but none of them read the device environment before a session even starts. Verihubs Device Intelligence sits upstream as a pre-risk layer, giving your existing fraud stack richer signals to work with. It's additive, not a replacement.
No. It reads device-level signals only: hardware characteristics, environment indicators, and behavioral patterns. Verihubs does not collect, store, or process personally identifiable information, which keeps compliance simpler for US platforms.
Zero friction. The SDK runs silently in the background. Legitimate users see and feel nothing different. The only change they notice is faster approvals, since your system has more confidence about the session.
App tampering itself is one of the signals Device Intelligence detects. If someone repacks or modifies your app to try removing or fooling the SDK, that modification is flagged as a risk signal on its own.
Root and jailbreak status contributes to the overall risk score, but Device Intelligence doesn't automatically block a session on its own. Your team sets the threshold, so you decide whether a rooted device alone should trigger manual review or be combined with other signals before any action is taken.
It is built primarily for mobile, iOS and Android, where device-level signals like emulators, root, and GPS spoofing are most relevant. For web-based onboarding flows, our team can advise on the right combination of checks.
Yes. Running Verihubs Device Intelligence with Verihubs ID Forgery Detection means a forged ID submitted from a suspicious device gets flagged twice, once for the environment, once for the document, giving your risk team a much clearer picture than either signal alone.