Root / Jailbreak Detection
Detects rooted Android and jailbroken iOS devices with OS-level security removed.

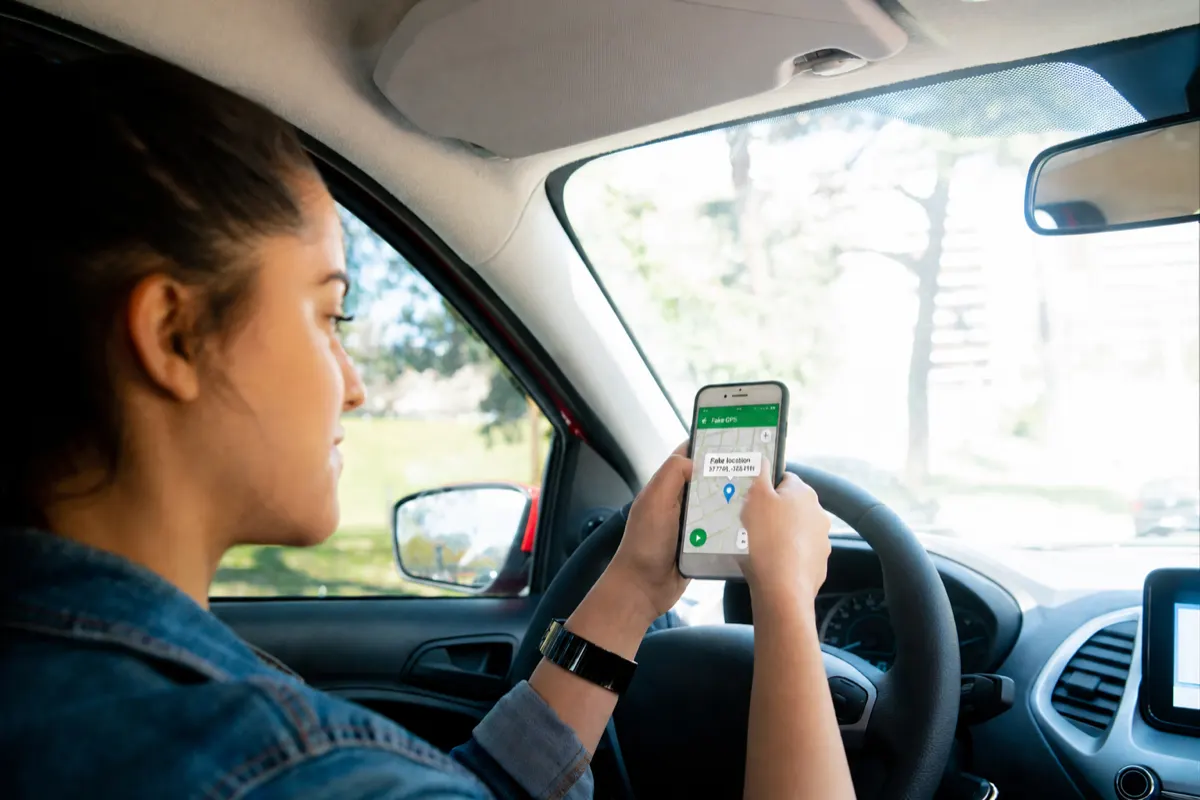
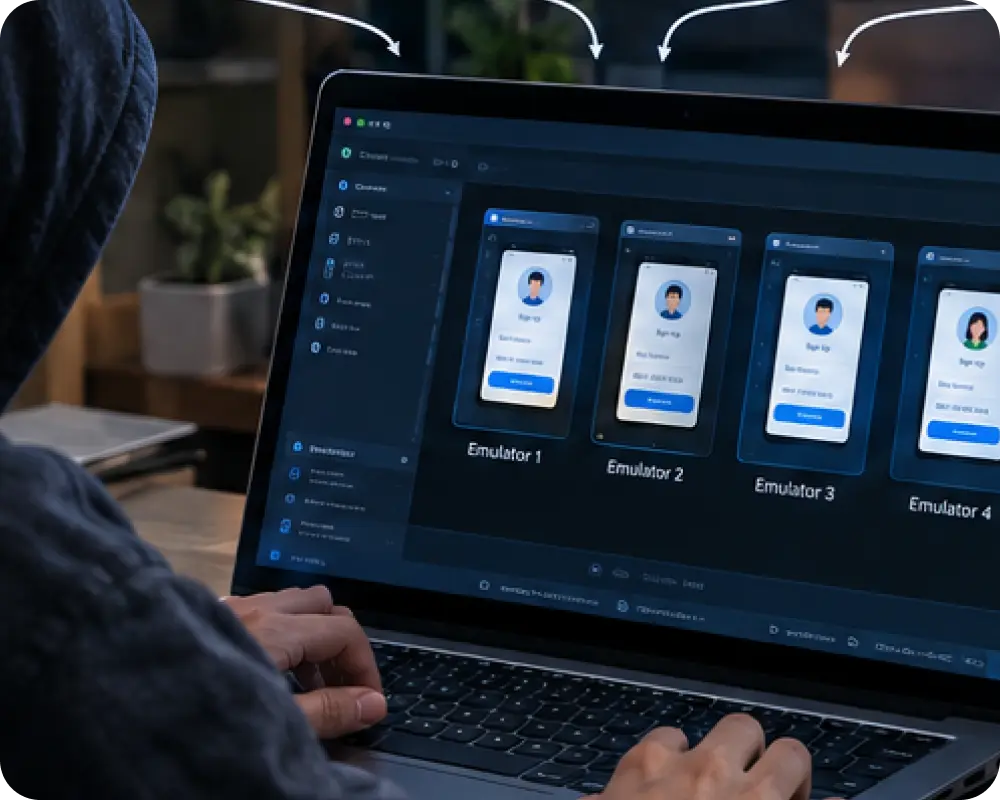
Stop identity theft and financial losses before they touch your system. Verihubs analyzes 15+ risk signals to identify emulators, fake locations, and malicious devices.

Fraud Prevention &
Account Security
Suspicious logins and ATO
Suspicious devices are flagged and blocked before they ever log in.
Compromised devices pass freely. ATO is discovered after the damage.
Multi-Account & Fake Account
Detection
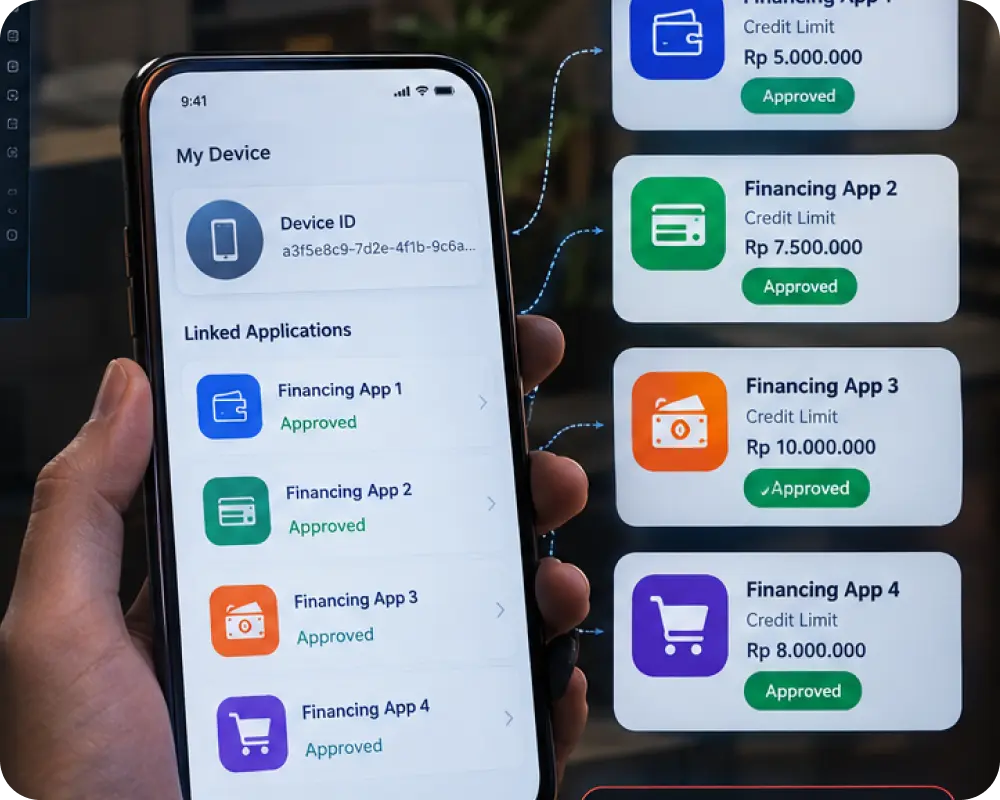
One device, many fake identities
One device creating multiple accounts is
identified as a suspicious pattern.
Every fake session looks like a brand new user. Promo abuse goes undetected.
KYC Strengthening &
Onboarding
Device context at registration
Device and location signals are cross-
checked before the first form field is filled.
KYC sees the identity. It has no visibility into the device behind it.
Why our Device Intelligence
How It Works
Checks run through the SDK in the background without adding steps to the user flow.
The Verihubs SDK runs in the background without loading screens or additional user steps, requiring no changes to your existing UX.
Verihubs reads emulator status, GPS integrity, root/jailbreak indicators, hooking frameworks, app tampering, and VPN usage to build a clear picture of how much the device can be trusted.
Analysis results are available as risk scores in your dashboard. Set rules to block, review, or approve based on detected risk signals, then monitor every result from one dashboard.
Use Case
Problems
Trading bots run on emulators to manipulate markets, rooted devices bypass withdrawal limits, and VPNs mask real locations to operate multiple fake accounts undetected.
Solutions
Detects emulators, root/jailbreak, VPN spoofers, hooking frameworks, and app tampering the moment the app opens. Active Call Detection also flags ongoing calls during login, trading, or withdrawals to help prevent social engineering fraud.
Use Cases: Account takeover • Fake accounts • Withdrawal fraud • Multi-accounting • Referral & bonus abuse • Social engineering fraud
Most fraud tools analyze behavior and identity, but none of them read the device environment before a session even starts. Verihubs Device Intelligence sits upstream as a pre-risk layer, giving your existing fraud stack richer signals to work with. It's additive, not a replacement.
No. It reads device-level signals only: hardware characteristics, environment indicators, and behavioral patterns. Verihubs does not collect, store, or process personally identifiable information, which keeps compliance simpler for US platforms.
Zero friction. The SDK runs silently in the background. Legitimate users see and feel nothing different. The only change they notice is faster approvals, since your system has more confidence about the session.
App tampering itself is one of the signals Device Intelligence detects. If someone repacks or modifies your app to try removing or fooling the SDK, that modification is flagged as a risk signal on its own.
Root and jailbreak status contributes to the overall risk score, but Device Intelligence doesn't automatically block a session on its own. Your team sets the threshold, so you decide whether a rooted device alone should trigger manual review or be combined with other signals before any action is taken.
It is built primarily for mobile, iOS and Android, where device-level signals like emulators, root, and GPS spoofing are most relevant. For web-based onboarding flows, our team can advise on the right combination of checks.
Yes. Running Verihubs Device Intelligence with Verihubs ID Forgery Detection means a forged ID submitted from a suspicious device gets flagged twice, once for the environment, once for the document, giving your risk team a much clearer picture than either signal alone.